
Personal Data
On this page you will find the latest regulations concerning personal data.
Since its entry into force on 25 May 2018, Regulation (EU) 2016/679 (General Data Protection Regulation, "GDPR") has consolidated the core principles of Directive 95/46/EC ("the Directive") and introduced enhanced obligations that fundamentally transform the personal data protection landscape throughout and beyond the EU.
Because we act in your interest and that of the Company, we are committed to respecting your personal data.
This personal data privacy policy (the "Policy") is intended to explain how Crédit Agricole CIB ("we") complies with this regulation in the context of managing its commercial activities with its corporate and institutional clients (or prospects) ("you"), as well as in the context of the related legal and regulatory obligations, by providing you with clear, detailed and comprehensive information on the processing we carry out on your personal data.
Crédit Agricole CIB does not commercialize your personal data under any circumstances.
CRÉDIT AGRICOLE CIB, DATA CONTROLLER
Operating within a regulated activity framework and acting as Data Controller, we offer and provide products and services that require the collection and use of your personal data and that of natural persons associated with you (including but not limited to: employees, shareholders, agents, legal representatives, beneficial owners, family members, third-party representatives...) (the "Data Subjects").
It is your responsibility to inform these Data Subjects about how we process their personal data.
Before transmitting personal data of a Data Subject to us, you undertake to have previously informed them of the content of this Policy and you assure us that we may collect, use and transmit this data according to the conditions established in the Policy.
PERSONAL DATA
To provide our services, we collect, use and potentially transmit personal data of several types:
• Civil status and identification data (surname, first name, date and place of birth, nationality, address/country of residence, passport and/or identity card number, photo, etc.)
• Personal life information (family situation, etc.)
• Professional life information (profession/function, employer, contact details, certifications/approvals, phone conversations/emails/chat, etc.)
• Economic and financial information (income, assets, tax situation, etc.)
• Technical information regarding use of our services (IP address, connection logs, cookies, etc.)
We collect only the data necessary to carry out our missions and ensure that their processing is performed in a fair, transparent manner and justified by an appropriate legal basis.
Personal data collection may be either direct, when shared by you, or indirect when we collect it from regulators or service providers.
PROCESSING PURPOSES
The processing operations we perform require the collection and use of personal data to:
• Comply with our legal and regulatory obligations (AMF, MAR, MiFID, AML/CFT, etc.)
• Manage Crédit Agricole CIB's risks relating to: anti-money laundering, counter-terrorist financing, fraud prevention, compliance with international sanctions
• Manage our internal control systems and whistleblowing mechanisms
• Manage commercial prospecting, conduct targeted commercial activities and event campaigns
• Manage business relationships (client management, correspondent designation, product marketing, etc.)
• Execute services or contracts within market activities (advisory activities, contract management with suppliers and clients, structured financing, banking flow and transaction management, placement activities, corporate finance, international activities, etc.)
LEGAL BASES FOR PROCESSING
In accordance with applicable regulations, we process personal data based on the following legal grounds, as applicable:
• Contract performance that we intend to conclude or have concluded with you, or
• Legal obligation requiring us to use personal data, such as in client knowledge management, prevention of money laundering and terrorist financing, compliance with embargoes and asset freezing measures, or
• Legitimate interest to collect personal data, for example in fraud prevention, or
• Your consent, for example for accepting a newsletter for communication purposes.
DATA RECIPIENTS
As a credit institution, we are bound by professional secrecy. However, in compliance with our banking secrecy obligations, we may communicate your personal data to recipients such as:
• Our entities within and outside the EEA
• Any Crédit Agricole Group entity for resource pooling or company consolidation purposes
• Our subcontractors solely for operational or technical subcontracting needs
• Independent agents, intermediaries or brokers
• French and foreign supervisory or regulatory authorities, French and foreign administrative and judicial authorities, public bodies upon request and within regulatory limits
• Certain regulated professions such as auditors, lawyers and notaries
When we engage subcontractors, we ensure they provide sufficient guarantees for GDPR-compliant processing and for ensuring personal data confidentiality and security.
PERSONAL DATA SECURITY
We place the security and confidentiality of your data at the heart of all our actions. We implement rigorous technical and organizational measures to guarantee a high level of protection during collection, processing and storage of your information, including:
• Access control and authorization management on IT equipment enabling personal data processing
• Security measures for technical infrastructure (workstations, networks, servers) and data (backup, business continuity plan)
• Privacy by design consideration in product or solution development
• Limitation of persons authorized to process personal data according to purposes and means defined for each processing operation
• Strict confidentiality obligations imposed on our subcontractors
• Awareness training for all our employees and in-depth training for employees most involved in personal data collection or management
• Implementation of procedures to respond promptly in case of personal data security incidents
DATA TRANSFER OUTSIDE THE EUROPEAN ECONOMIC AREA (EEA)
To execute our services or satisfy our legal and regulatory obligations, we may transfer Data Subjects' personal data to countries outside the EEA.
In such cases, Crédit Agricole CIB ensures that the recipient is subject to local legislation ensuring an adequate level of protection or to guarantees ensuring this level of protection.
These guarantees may include Standard Contractual Clauses for personal data protection adopted by the European Commission (i.e., a transfer contract between the data controller and a recipient specifying the obligations of both parties in case of personal data transfer outside the European Union).
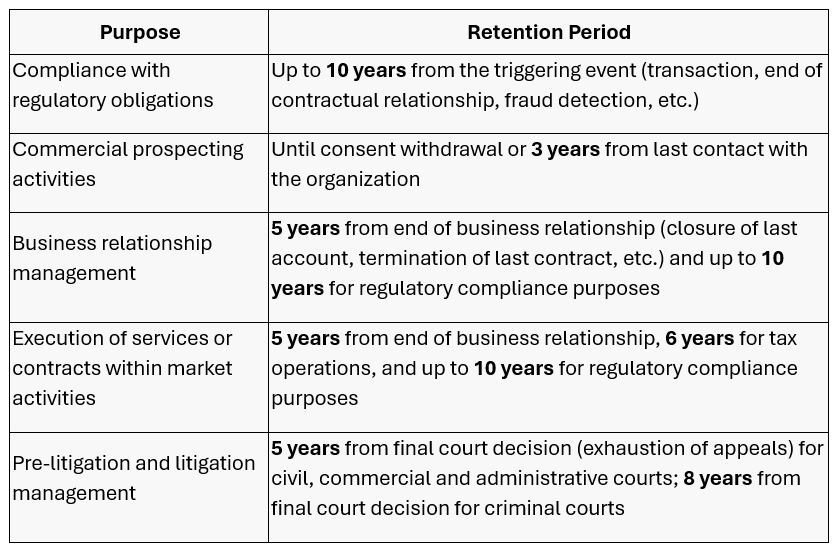
DATA RETENTION PERIOD
We retain Data Subjects' personal data for the duration necessary to achieve the intended purpose.
Below are the retention periods for your personal data according to different processing purposes:
EXERCISING YOUR RIGHTS
We ensure that each client maintains full control over their personal data.
In accordance with the General Data Protection Regulation (GDPR), you may exercise the following rights at any time:
• Access your data and obtain a copy
• Correct or complete your data
• Request deletion when data is no longer necessary
• Temporarily limit data use
• Object to certain processing operations (e.g., commercial prospecting)
You may exercise these rights:
• Through your relationship manager or usual commercial contact,
• By writing to : Crédit Agricole CIB – Direction de la Conformité / Data Protection – 12, place des Etats-Unis – 92127 Montrouge Cedex,
• By email to the Data Protection Office at dcp@ca-cib.com.
When submitting a rights exercise request, to facilitate review and enable prompt response, please specify as much as possible: (i) the scope of the request, (ii) the nature of the request/type of right exercised, (iii) the personal data processing concerned, and any other useful contextual information.
You will be required to provide proof of identity.
MISCELLANEOUS
We use cookies to better understand how our site is used by our visitors and to improve your browsing experience. For more information, including how to configure cookies, please see the "Cookies" section in our legal notice.
POLICY UPDATES
This Policy is regularly updated to consider regulatory evolutions and the processing we operate.
Last update : September 16, 2026